155 GLM Replies Crossed Tenants. There Is No CVE.
155 GLM 5.3 replies held another tenant's cache, Cloudflare says. Restored 9 September. Public post 26 October. SGLang 0.5.22 is on PyPI. There is no CVE.
CVE-2026-92206 went public on 21 October, 35 days after its public date. The record names no patched release. PyPI 1.15.28 is absent from that field.
ZDI published CVE-2026-92206 on 21 October 2026 at 17:17 UTC. The record's public date is 16 September at 15:11 UTC, and it names no patched version. GitHub advisory GHSA-pgwr-r23p-38mr followed at 18:33 UTC with an empty version list. PyPI's current release is crewai 1.15.28 from 14 October, which the CVE does not mention. The repository advisory list is empty.
US trends at 22:40 UTC were Tom Skerritt, Lindsey Graham, and Thursday Night Football. Hacker News led with Quad9 leaving France. The primary here is CVE-2026-92206, published by ZDI at 17:17:33.262 UTC on 21 October 2026. The September brief filed this under ZDI-26-706 and left the CVE number off until a record existed. The record exists. The pin does not.
High High because the record's own score is CVSS 3.0 base 8.8, CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:H/A:H, CWE-470. User interaction is required. The package field still has nothing an installer can pin.
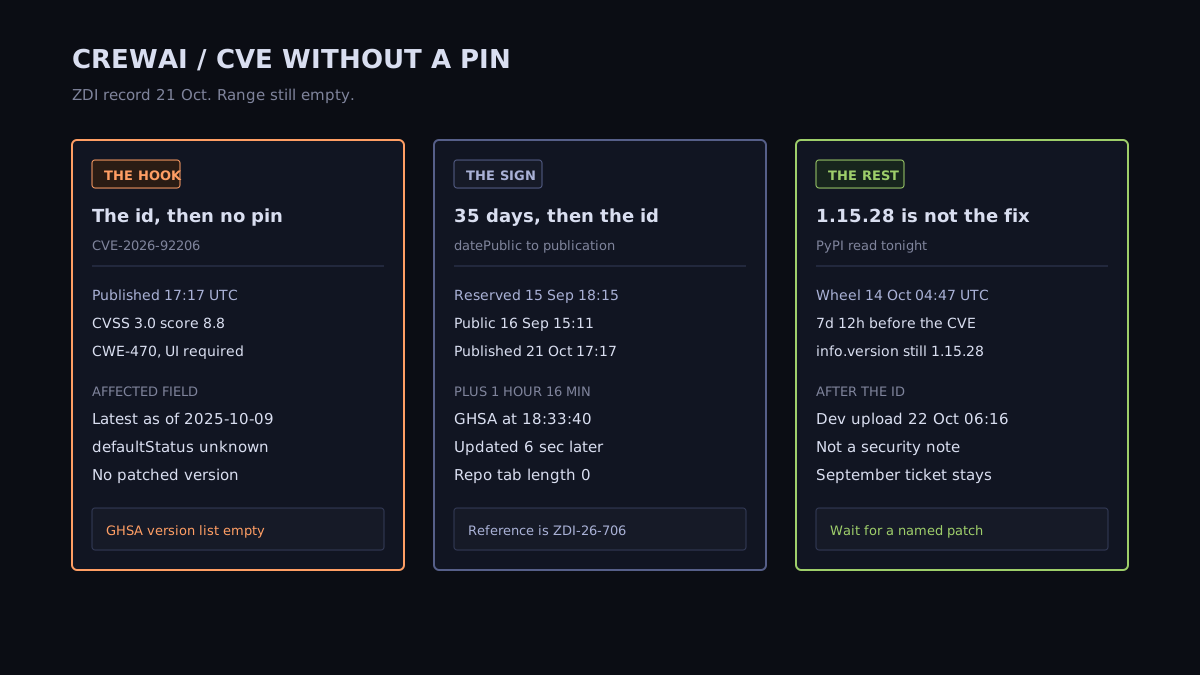
The cveawg record is state PUBLISHED. dateReserved is 2026-09-15T18:15:32.922Z. datePublished and dateUpdated are both 2026-10-21T17:17:33.262Z. Reserve to publication is 35 days 23 hours 2 minutes. datePublic is 2026-09-16T15:11:00.748Z. Public date to publication is 35 days 2 hours 6 min 32.514 sec. The assigner short name is zdi.
The affected product is CrewAI by CrewAI. The only version object is Latest (as of 2025-10-09), status affected. defaultStatus is unknown. There is no lessThan, no introduced semver, and no patched version. The date inside that string is 9 October 2025. It is not a build this brief can resolve on PyPI.
The description matches the ZDI title the September brief used: agent loading, unsafe reflection, remote code execution, user interaction required because the target loads an agent configuration from the repository. It names load_agent_from_repository. It ends with the sentence "Was ZDI-CAN-28387." The references array has one URL, https://www.zerodayinitiative.com/advisories/ZDI-26-706/, tag x_research-advisory. This brief did not re-fetch that page. The CAN id and the 26-706 id both appear on this CVE record. They are not two version ranges.
GHSA-pgwr-r23p-38mr published at 2026-10-21T18:33:40Z and updated at 2026-10-21T18:33:46Z. That is 1 hour 16 min 6.738 sec after the CVE. Severity on the GHSA is high. The CVSS object is the same 3.0 vector at 8.8. CWE-470. The summary is the CVE text, cut off in the API's summary field and complete in the description, including the CAN sentence. vulnerabilities is an empty array. There is no package name, no range, and no patched version on the GHSA either. Credits are empty. A read of crewAIInc/crewAI security-advisories returns length 0. The id lives in the GitHub Advisory Database. It does not live on the repository advisory tab.
A PyPI read tonight: info.version is 1.15.28. The wheel uploaded at 2026-10-14T04:47:37.463658Z. The sdist uploaded at 2026-10-14T04:47:39.602233Z. Neither file is yanked. That upload is 7 days 12 hours 29 min 55.798 sec before datePublished. It is also after the 16 September public date. The September brief's open fact was the missing patch URL. A later stable upload, by itself, is not that URL.
The only release file with an upload time after the CVE is 1.15.28.dev20261022, at 2026-10-22T06:16:54.110059Z, not yanked. It is not info.version. The dev uploads on 19, 20, and 21 October are the same shape, a date stamp under 1.15.28, and the 21 October dev file is 06:16 UTC, before the CVE. This brief did not read those changelogs and did not treat a dev stamp as a security note. The record does not name any of them.
From the public date to this stable upload is the gap the old ticket already had: ZDI-26-706 was public, and no vendor build was named. From the stable upload to the CVE is a new gap: a release shipped, then the identifier arrived, and the identifier still does not point at a release. Reserve day is 15 September, the day before datePublic. The package clock the operator can act on is still missing.
The September brief keeps the ZDI narrative, the 8.8 score, and the user-interaction condition. This page adds the clocks on the record. It does not replace that write-up, and it does not import a reproduction. The CVE text is the whole behavior claim used here: a user loads an agent configuration from the repository, and load_agent_from_repository imports from that argument. Code runs as the service account. That is the record's wording.
crewai==1.15.28 as a remediation pin. It is the current PyPI release, the wheel is from 14 October, and neither the CVE nor the GHSA names it. When a patched version appears, it has to appear on the record.1.15.28.dev20261022 to get ahead of the id. It is a dev upload after publication. info.version did not move to it. The file is not a security advisory.crewAIInc/crewAI security advisories still returns nothing. The GitHub Advisory Database row is the one with the id.datePublic.The CVE does not say so. Its only affected entry is the string Latest (as of 2025-10-09), status affected, and it has no patched version. PyPI info.version tonight is 1.15.28, uploaded 14 October, 7 days 12 hours before the CVE. A version that predates the record is not a fix the record forgot to name.
The CVE description ends with Was ZDI-CAN-28387. The references array has one URL, the ZDI-26-706 page, tagged as the research advisory. datePublic matches 16 September 2026. Those are two identifiers on one record. This brief does not open a second bug for the CAN id, and it does not pretend the record explains the rename.
The cveawg record is state PUBLISHED. GHSA-pgwr-r23p-38mr is a reviewed GitHub Advisory Database entry with that CVE id, an 8.8 score, and an empty vulnerabilities array. The crewAIInc/crewAI security-advisories API returns length 0. The id is public. The pin is missing. Those are different lists.
155 GLM 5.3 replies held another tenant's cache, Cloudflare says. Restored 9 September. Public post 26 October. SGLang 0.5.22 is on PyPI. There is no CVE.
Qwen3.8-Flash-Next tried to upload after its reasoning said no tools. Cohere's sandbox blocked it. Under one eval call in 100,000. No CVE and no weight hash.
A Downloads instruction file sent Codex toward function-color. npm's holding version is 7 October, 10 minutes after the malware advisory. There is no agent CVE.