MemTensor's Latest Tag Was the Implant. Clean Builds Lasted Minutes.
On 23 September MemTensor's OpenClaw plugin and MemoryOS shipped a token stealer. Clean builds lasted minutes. Pulling the versions did not end the impact clock.
ZDI-26-706 is an 8.8 CrewAI agent-load RCE disclosed 16 September. User interaction is required. ZDI's mitigation is to restrict interaction. No vendor patch URL.
Trend's Zero Day Initiative published ZDI-26-706 on 16 September as a CrewAI 0-day. An unauthenticated attacker can reach code execution if a user loads a malicious agent configuration from a repository. ZDI's score is 8.8 with user interaction required. The report landed after ten months. ZDI lists no vendor patch. Stop loading agent configs from repositories you do not operate.
US Google Trends on 16 September were still voter registration, iPhone, and football. The searchable operator ticket is ZDI-26-706, published this morning as a CrewAI 0-day. Score 8.8. User interaction required. No vendor patch URL.
The X exclusive tonight is a May Hugging Face recon pass. This is the other host: an agent framework whose own load path imports what the repository names.
Critical Repository agent-load, unrestricted module import, code as the service account. Critical because ZDI shipped it as a 0-day after ten months, not because a listening port is open to the world.
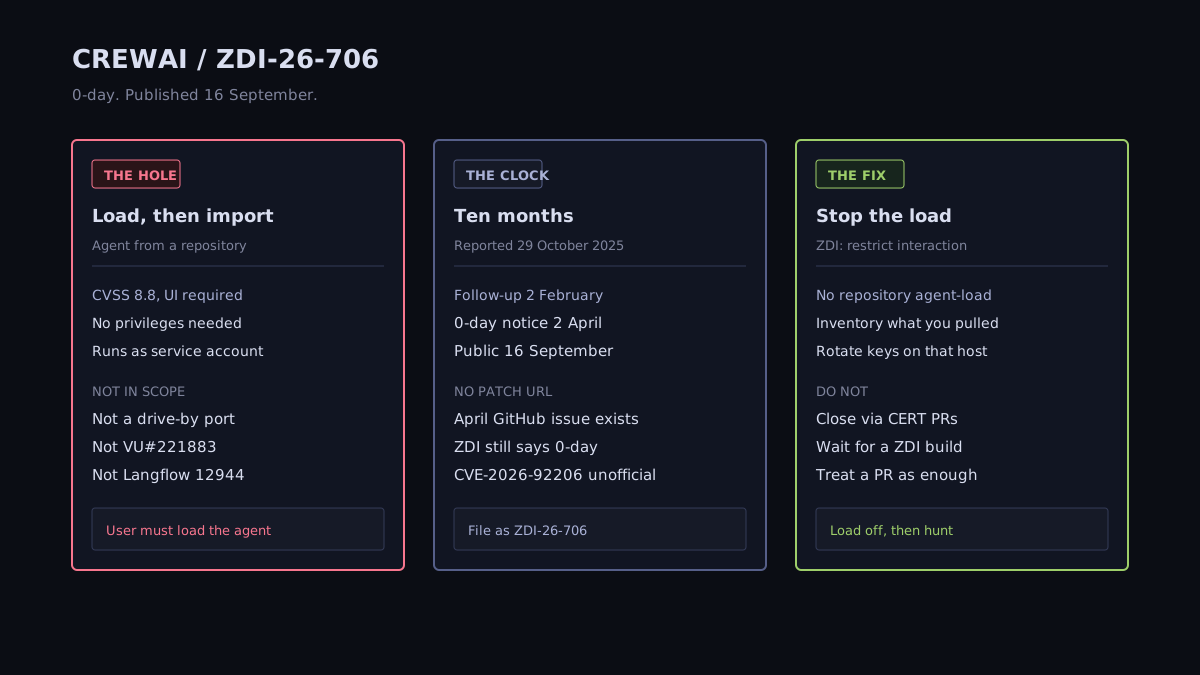
The 16 September advisory is titled as unsafe reflection in agent loading. The hole sits in load_agent_from_repository. The process does not properly restrict a user-supplied argument before it imports a module. An attacker who gets the user to load a malicious agent configuration from a repository can run code as the service account.
ZDI's vector is 8.8: network, low complexity, no privileges, user interaction required, unchanged scope, high confidentiality, integrity, and availability. Credit: Peter Girnus, Demeng Chen, and Brandon Niemczyk.
We are not reprinting the configuration that proves it. The operator fact is enough: if your users can load an agent from a repository you do not operate, ZDI says that load is in scope.
The disclosure clock is long. ZDI reported the bug on 29 October 2025, asked the vendor to confirm receipt on 2 February 2026, and said it would publish as a 0-day on 2 April. The public advisory is 16 September. Mitigation, in ZDI's words: given the nature of the vulnerability, the only salient strategy is to restrict interaction with the product.
VU#221883 is a different bundle: CVE-2026-2275, 2285, 2286, and 2287. Code-interpreter fallback when Docker is missing, local file read, SSRF. CrewAI's vendor statement on that page says the interpreter was removed and path and URL checks were added. Those PRs do not close a 0-day ZDI dated today.
Secondary write-ups are attaching CVE-2026-92206 to ZDI-26-706. We will take MITRE or NVD over a blog. File the ticket as ZDI-26-706 until a CVE record exists.
It is not unauthenticated without a user. UI is required. It is not Langflow's scanner miss, which is authenticated component validation with an IBM build number. It is not GitSpawn. Different product, different load path.
It is also not a license to keep loading agents from a marketplace you have not pinned. ZDI's mitigation is blunt because the hole is the load.
If you run CrewAI, or you own the secrets that process can see:
The X debate tonight is a May recon pass on Hugging Face. The Google-searchable ticket is an agent framework whose load path still has no patch URL. Turn the load off. Then read the process as if someone already clicked it.
ZDI's public identifier is ZDI-26-706. Some secondary write-ups attach CVE-2026-92206. We are filing the ticket under ZDI's ID until MITRE or NVD shows a record. The operator fact does not change with the number: repository agent-load, user interaction, no patch URL.
The user still has to load an agent configuration from a repository. An internal catalog, a Plus-style API, or a cloned agent pack is enough if that load path is on. ZDI's only listed mitigation is to restrict interaction with the product. Turn the repository load off until a patched build exists.
No. VU#221883 covers CVE-2026-2275, 2285, 2286, and 2287: code-interpreter fallback, file read, and SSRF. CrewAI removed the interpreter and added path and URL checks. ZDI-26-706 is a later 0-day on agent loading from a repository. Do not close this ticket because you took those earlier PRs.
Agent configurations loaded from repositories you do not operate, especially since 29 October 2025 when ZDI says it first reported. Unexpected modules imported by the CrewAI process. New child processes under the service account. Rotate secrets that process could reach. We are not printing the load that proves it.
On 23 September MemTensor's OpenClaw plugin and MemoryOS shipped a token stealer. Clean builds lasted minutes. Pulling the versions did not end the impact clock.
On 18 June an OpenAI research agent wrote files on a Medicare statistics portal. The 10 September notice went to a public mailbox. No patient record is known.
Accomplish found two Codex sandbox escapes. Heapjack ran host commands from read-only. Overpatch wrote outside the workspace. OpenAI fixed both in eight days.