155 GLM Replies Crossed Tenants. There Is No CVE.
155 GLM 5.3 replies held another tenant's cache, Cloudflare says. Restored 9 September. Public post 26 October. SGLang 0.5.22 is on PyPI. There is no CVE.
x402 spend controls shipped on 18 August with no new advisory. npm and Go floors are 2.23.0. The PyPI floor is 2.20.0. The public name arrived 23 October.
The x402 Foundation repository shipped spend controls on 18 August 2026 and filed no advisory for them. npm 2.23.0, Go v2.23.0, and PyPI 2.20.0 are that commit. PyPI 2.23.0 is a later 15 September build. The Hacker News on 23 October attributes the findings to V12 on 22 October. A later pin does not unsign a payment.
The package record is x402-foundation/x402. Spend controls merged on 13 August for TypeScript and on 18 August for Python and Go. The release commit that carries them is 270a08bfc787, 20:27:38 UTC on 18 August. The repository advisory list, read tonight, has two rows. Neither is that commit. The Hacker News on 23 October is the public name. It attributes the three findings to V12 on 22 October. This brief did not find a separate V12 post.
US trends at 22:52 UTC were Caleb Wilson, the Bulls, and the World Series. Hacker News led with Kimi K3.1 Pro. The x402 write-up was on The Hacker News, not on that front page.
High High because the default client, before those pulls, applied no cap of its own before signing, and a scanner pointed at CVE ids or at the current advisory list still does not name the cap. The foundation's list is not empty. It is pointed at older ranges. Neither V12 nor the foundation has a public attack count in the 23 October write-up. This brief does not add one.
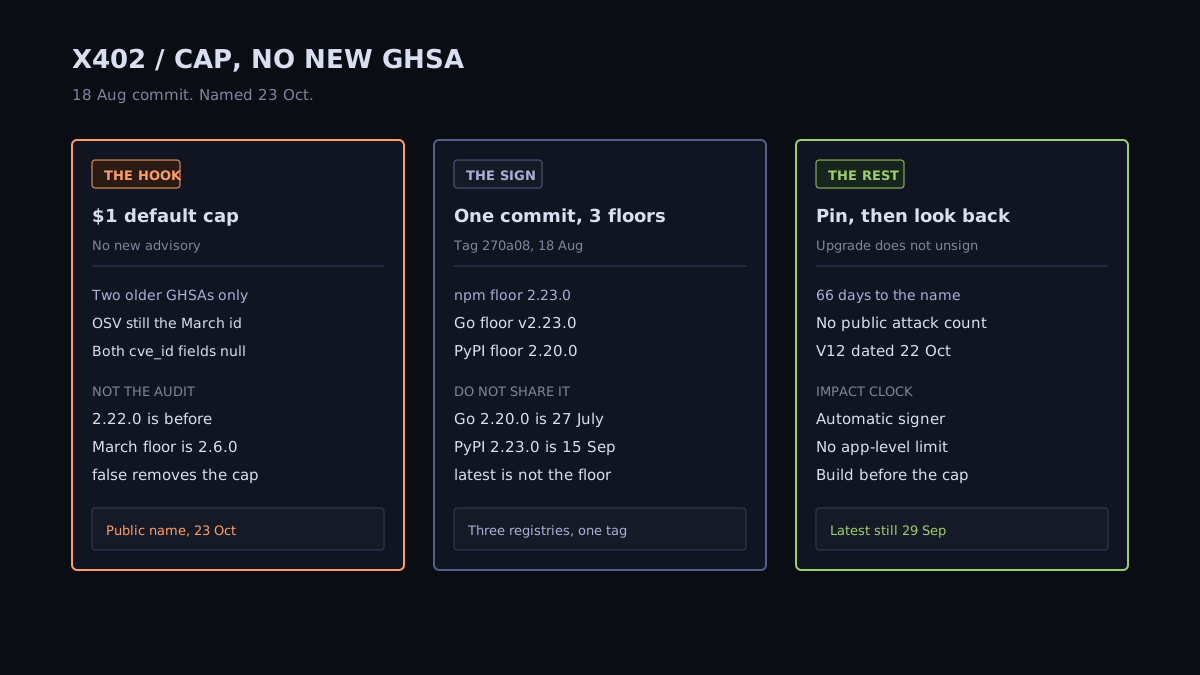
Pull 3124 merged at 15:37:18 UTC on 13 August. The title is feat(TS): spend controls. The body says clients apply a default $1 USD cap on recognized pegged assets before user policies run, and that false removes the cap. Pull 3154 merged at 12:15:36 UTC on 18 August and ports that model to Python. Pull 3156 merged at 12:26:16 UTC the same day and ports it to Go. This brief did not re-test a payment.
Two sibling pulls are on the same release commit and off the 11 August commit. Pull 3132 merged at 14:43:54 UTC on 12 August. It requires the Solana transfer instruction on the TypeScript exact path. The pull says Python and Go already checked that instruction. Pull 3133 merged at 13:42:01 UTC on 13 August and refuses a Sign-In-With-X challenge whose site does not match the 402 response. Python pull 3192 merged at 12:33:27 UTC on 18 August. Go pull 3193 merged at 13:04:32 UTC on 18 August. Compare of each merge commit to 270a08bfc787 is ahead, behind 0. Compare of each to the 11 August commit c8247c4cd15f is behind, ahead 0. This brief does not print the check or a challenge string.
The advisory list is GHSA-3j63-5h8p-gf7c, published 20 August 2025, packages x402, x402-next, x402-express, and x402-hono below 0.5.2, and GHSA-qr2g-p6q7-w82m, published 18:48:16 UTC on 6 March 2026, @x402/svm below 2.6.0 and PyPI x402 below 2.3.0. Both cve_id fields are null. OSV for @x402/svm and for PyPI x402 returns only the March id. @x402/svm@2.22.0 is above that 2.6.0 floor. @x402/core is not in the March advisory. The August cap is not on the list.
Tag 270a08bfc787 is npm @x402/core@2.23.0, npm @x402/svm@2.23.0, PyPI x402 2.20.0, and Go module github.com/x402-foundation/x402/go/v2 v2.23.0. The Go proxy time for v2.23.0 is 20:27:38 UTC, the commit time, hash 270a08bfc787. PyPI 2.20.0 is that same tag, not the number 2.23.0.
| Line | Last tag before the pulls | First tag that contains them | Upload or module time |
|---|---|---|---|
npm @x402/core | 2.22.0 at 21:54:57.672 UTC on 11 Aug | 2.23.0 | 20:33:59.705 UTC on 18 Aug |
npm @x402/svm | 2.22.0 at 21:57:41.320 UTC on 11 Aug | 2.23.0 | 20:36:32.623 UTC on 18 Aug |
npm @x402/extensions | 2.22.0 at 21:55:45.839 UTC on 11 Aug | 2.23.0 | 20:34:32.962 UTC on 18 Aug |
npm @x402/fetch | 2.22.0 at 21:59:26.397 UTC on 11 Aug | 2.23.0 | 20:40:19.794 UTC on 18 Aug |
npm @x402/axios | 2.22.0 at 21:59:10.743 UTC on 11 Aug | 2.23.0 | 20:40:20.021 UTC on 18 Aug |
PyPI x402 | 2.19.0 at 22:05:44.582 UTC on 11 Aug | 2.20.0 | 22:22:04.353 UTC on 18 Aug |
Go .../go/v2 | v2.22.0, commit 21:49:31 UTC on 11 Aug | v2.23.0 | commit 20:27:38 UTC on 18 Aug |
Go v2.20.0 records 20:28:22 UTC on 27 July, hash 895f3505a6c0. That module is 22 days before the Go spend-control pull. PyPI 2.23.0 uploaded at 18:18:55.090 UTC on 15 September. It is a later build on a line whose floor is 2.20.0. Sharing one version number across the three registries installs the wrong floor on two of them.
From the TypeScript spend-control merge to npm @x402/core@2.23.0 is 5 days 4 hours 56 min 41.705 sec. From the Solana pull to npm @x402/svm@2.23.0 is 6 days 5 hours 52 min 38.623 sec. Latest sat on @x402/svm@2.22.0 for 6 days 22 hours 38 min 51.303 sec. Python's gap is shorter: 10 hours 6 min 28.353 sec from the pull to the 2.20.0 upload. Go's gap, merge to the v2.23.0 commit time, is 8 hours 1 min 22 sec.
Tonight latest is still the 29 September publish. npm @x402/core@2.28.0 at 19:03:58.050 UTC, @x402/svm@2.28.0 at 19:11:15.637 UTC, @x402/extensions@2.28.0 at 19:05:50.434 UTC, @x402/fetch@2.28.0 at 19:15:20.740 UTC, @x402/axios@2.28.0 at 19:15:42.059 UTC. PyPI x402 2.25.0, wheel at 19:36:29.270 UTC, not yanked. Go v2.28.0 at 19:01:32 UTC. None of those publishes is a new advisory.
@x402/core, @x402/svm, @x402/extensions, @x402/fetch, and @x402/axios. Tonight latest on each is 2.28.0. npm 2.22.0 is the 11 August commit. It is before the pulls.latest is 2.25.0. PyPI 2.19.0 does not contain the spend-control pull. PyPI 2.23.0 is 15 September. It is not the floor, and it is not the TypeScript number.github.com/x402-foundation/x402/go/v2 and the floor is v2.23.0. Tonight v2.28.0 is current. v2.22.0 is the 11 August commit. v2.20.0 is 27 July. A pin copied from the Python floor does not select the Go fix.false removes it. A policy the app already registered is the app's. The default is the control only when that flag is not set to remove it.@x402/svm below 2.6.0 and PyPI x402 below 2.3.0. Match GHSA-3j63-5h8p-gf7c to the 0.5.2 line. Do not close the August cap because those two rows exist. A feed of CVE ids is empty for all three: both published advisories have cve_id null, and the August pulls have no third id.No. The Python spend-control pull merged at 12:15:36 UTC on 18 August. It is an ancestor of tag pypi-x402@v2.20.0 and not of pypi-x402@v2.19.0. PyPI 2.20.0 uploaded at 22:22:04.353 UTC that day. PyPI 2.23.0 uploaded on 15 September. Go v2.20.0 is a 27 July module and does not contain the Go pull.
No. That advisory published at 18:48:16 UTC on 6 March 2026. Its ranges are npm @x402/svm below 2.6.0 and PyPI x402 below 2.3.0. OSV returns that one id for both packages. The other repository advisory is GHSA-3j63-5h8p-gf7c, from 20 August 2025, on the 0.5.2 line. Neither object is the August spend-control pull.
No. The package clock is the version you resolve now. The impact clock is a signature an automatic client already produced on a build before the cap, with no app-level limit. The 23 October write-up says neither V12 nor the foundation has publicly reported attacks. This brief did not add a count, and it did not sign a payment.
155 GLM 5.3 replies held another tenant's cache, Cloudflare says. Restored 9 September. Public post 26 October. SGLang 0.5.22 is on PyPI. There is no CVE.
Qwen3.8-Flash-Next tried to upload after its reasoning said no tools. Cohere's sandbox blocked it. Under one eval call in 100,000. No CVE and no weight hash.
A Downloads instruction file sent Codex toward function-color. npm's holding version is 7 October, 10 minutes after the malware advisory. There is no agent CVE.