155 GLM Replies Crossed Tenants. There Is No CVE.
155 GLM 5.3 replies held another tenant's cache, Cloudflare says. Restored 9 September. Public post 26 October. SGLang 0.5.22 is on PyPI. There is no CVE.
Tensorlake npm 0.5.144 shipped from main with a signed preinstall hook. npm removed that SDK version the same day. Six native 0.5.144 packages were still listed.
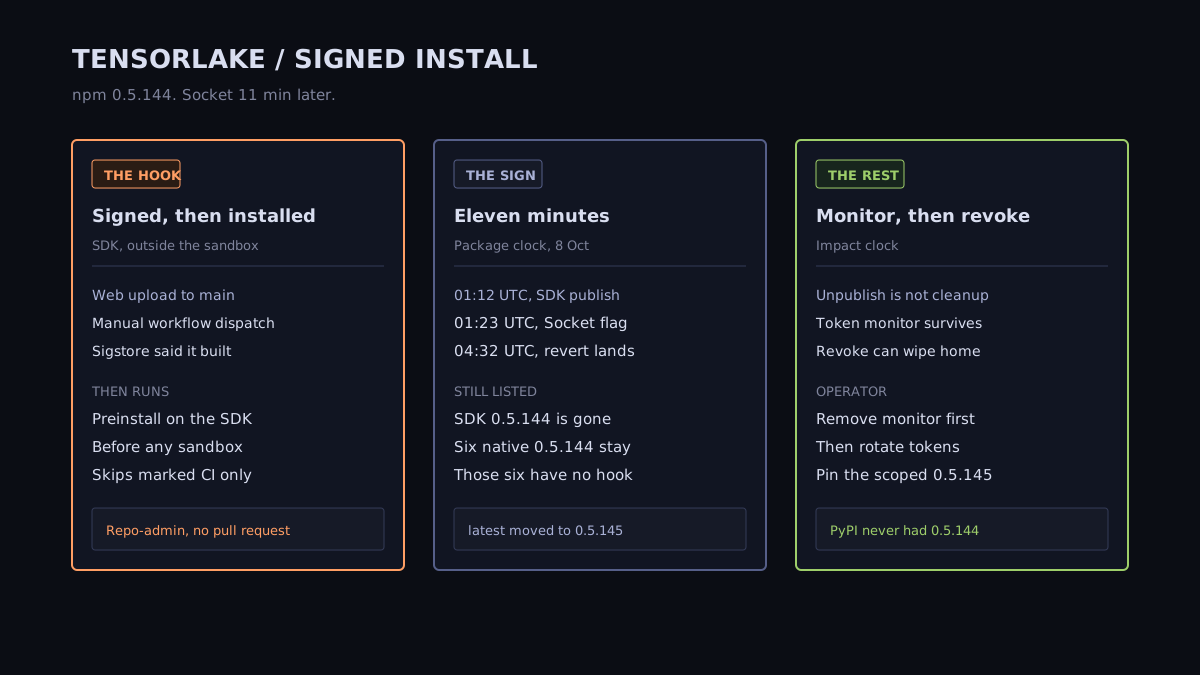
Tensorlake npm 0.5.144 published at 01:12 UTC on 8 October from the project's main branch, with Sigstore provenance and a preinstall hook. Socket flagged it 11 minutes later. npm then removed that SDK version. The maintainer revert merged at 04:32 UTC. Six native 0.5.144 packages were still listed that night. A host that ran the hook is still in scope.
Tensorlake npm 0.5.144 published at 01:12:07 UTC on 8 October from the project's own main branch, and the release workflow signed it. Socket flagged the tarball at 01:23:10 UTC. Pull request 1016, merged at 04:32 UTC, is the maintainer's account: a repo-admin web upload, a manual dispatch of publish_npm.yaml, Sigstore provenance, and npm already removing that SDK version.
Hacker News on 8 October led with speech-to-text, a DeepSeek thread, and a Microsoft visa story. US X trends were baseball, H-1B, and celebrity names. The operator fact was the install hook.
High A signed release of an agent-sandbox SDK ran code at install time. High because the hook fires before any sandbox, and because revoking the stolen GitHub token first can wipe the machine that still has the monitor.
Tensorlake ships sandboxes for untrusted, model-written code. The npm package is the TypeScript SDK those sandboxes are created from. Socket puts weekly downloads around 12,000 and says that number is the package, not this version. Nobody has published a count of machines that ran the hook.
The git path is in the maintainer's own incident note. Commits e90c47bb through 6386121c landed on main from a repo-admin account through the GitHub web UI. The first of those, e90c47bb, is "Add files via upload" at 01:20:15 UTC on 7 October. Four minutes later, c79bc47554 adds the preinstall line. The tip of that range, 6386121c at 23:41 UTC, is "fix: platform package versions to 0.5.144". On that commit, typescript/package.json sets preinstall to node lib/setup.mjs. None of those commits is a reviewed pull request.
The publish was not a mystery pipeline. Pull request 1016 says a person manually dispatched publish_npm.yaml. That workflow built the package from main and signed it with Sigstore. npm provenance was valid because the workflow was the project's workflow. StepSecurity filed GitHub issue 1014 at 01:22:02 UTC, ten minutes after the registry time on 0.5.144.
Socket's read of the published manifest is that the preinstall runs when the package is installed, before anyone imports the SDK or starts a sandbox. The sandbox is the product the SDK is supposed to call. It is not the process that runs npm install. Sonatype says the loader exits when CI is true or 1, when GITHUB_ACTIONS or GITLAB_CI is true, or when RUNNER_ENVIRONMENT is github-hosted. A laptop, and a self-hosted runner that does not set those markers, is the target StepSecurity describes.
The code, as those three firms read it, collects npm and GitHub tokens, cloud keys, Kubernetes and Vault secrets, SSH keys, and config for Claude, Cursor, Windsurf, Zed, and Kiro. It can open a public GitHub repo described "Shai-Hulud: Here We Go Again", and it can commit .claude and .vscode files under claude@users.noreply.github.com. Sonatype is explicit that it has not confirmed stolen data was published, that those repos were modified, or that any downstream package was republished. Treat the spread as a capability until a release you did not cut shows up.
The package clock is the registry. The impact clock starts the moment the hook runs, and it outlives the version npm removed.
A check of the public npm registry later on 8 October matches the maintainer note on the SDK and not yet on the natives. tensorlake@0.5.144 is gone from the version list. The time record is still 01:12:07 UTC, which is Socket's publish timestamp. latest is 0.5.145, published 20:24 UTC, and it depends on @tensorlakeai/tensorlake@0.5.145. That scoped release, at 20:20 UTC, has no preinstall. Its scripts include check:install-scripts. Pull request 1017, merged 19:58 UTC, is the move into the @tensorlakeai scope and staged publishing that requires a maintainer's 2FA before a version goes public.
The six packages the revert said still had to be unpublished were still listed on that same read: tensorlake-native-darwin-arm64, tensorlake-native-linux-arm64-gnu, tensorlake-native-linux-arm64-musl, tensorlake-native-linux-x64-gnu, tensorlake-native-linux-x64-musl, and tensorlake-native-win32-x64, each at 0.5.144, with publish times from 00:17 to 00:19 UTC. None of those six manifests declares an install script. Their latest tag is already 0.5.145. Absence of a hook is not the same as a version the maintainer wanted left up.
PyPI's tensorlake project has wheels for 0.5.143 and 0.5.145 and no 0.5.144 release. The 0.5.145 wheels uploaded at 20:37 UTC. Aikido saw no publish on Cargo. The npm SDK is the release that carried the hook.
It is not a breakout from a Tensorlake sandbox. The malicious code runs in the install, on the developer machine or the runner, with the rights of that process. Code the sandbox was built to contain has not started yet.
It is not proof that the August ChainDrop wave already owned this repository. Socket says the loader shape matches that wave. Aikido says a marker on this package makes it a new compromise. Either reading ends at the same action: treat hosts that installed 0.5.144 as compromised, and review packages those hosts were allowed to publish.
It is not a reason to keep StepSecurity's interim pin to 0.5.143 as the end state. That pin was right while 0.5.144 was still the fresh release and 0.5.145 did not exist. The replacement is 0.5.145 on the scoped name, or the unscoped wrapper that pins the same version. Anything still versioned 0.5.144 stays uninstalled.
tensorlake@0.5.144 and for the six native names at that version. A transitive pin counts. The SDK version missing from npm view does not mean a laptop never fetched it.gh-token-monitor. Back up what you cannot lose before you delete it. Revoke only after that service is gone..env files, and the AI tool configs Socket lists: Claude, Cursor, Windsurf, Zed, and Kiro. A marked GitHub-hosted runner skips the hook. A job that does not set those markers does not.claude@users.noreply.github.com with the message "chore: update dependencies", and .claude or .vscode files nobody on the team added. Sonatype has not confirmed those writes happened. The hunt is how you find out.@tensorlakeai/tensorlake@0.5.145. Keep install scripts off for this dependency until you have diffed the tarball. The project's own CI now installs with scripts ignored, and pull request 1016 adds a tripwire that fails the build if a published manifest grows an install hook.A read of the public npm registry on 8 October showed unscoped latest at 0.5.145, published 20:24 UTC, and 0.5.144 absent from the version list. That 0.5.145 is a wrapper onto @tensorlakeai/tensorlake at the same version. The scoped manifest has no preinstall. It does not clear a machine that already installed 0.5.144, and it does not unpublish the six native packages that are still at that version.
No. Maintainer pull request 1016 says the release was a manual dispatch of publish_npm.yaml, which built the package from main and signed it. The attestation records that workflow. The commits it built were web uploads by a repo-admin account. Provenance passed because the pipeline ran, not because the diff was clean.
Remove the token monitor first. StepSecurity and Socket both say the monitor polls the stolen GitHub token and, if GitHub rejects it, wipes the home directory. Revoking from the GitHub settings page still trips a monitor left on the laptop. After the monitor is gone, rotate npm, GitHub, cloud, Kubernetes, Vault, SSH, and the AI tool credentials that process could read.
PyPI lists 0.5.143 and 0.5.145 and has no 0.5.144 release. The 0.5.145 wheels uploaded at 20:37 UTC. Aikido saw no Cargo publish. On npm, the six tensorlake-native 0.5.144 packages were still listed the same night, and their manifests declare no install scripts. The preinstall line was on the SDK package. Leave the native 0.5.144 versions uninstalled anyway. The maintainer asked for them to be unpublished.
155 GLM 5.3 replies held another tenant's cache, Cloudflare says. Restored 9 September. Public post 26 October. SGLang 0.5.22 is on PyPI. There is no CVE.
Qwen3.8-Flash-Next tried to upload after its reasoning said no tools. Cohere's sandbox blocked it. Under one eval call in 100,000. No CVE and no weight hash.
A Downloads instruction file sent Codex toward function-color. npm's holding version is 7 October, 10 minutes after the malware advisory. There is no agent CVE.