155 GLM Replies Crossed Tenants. There Is No CVE.
155 GLM 5.3 replies held another tenant's cache, Cloudflare says. Restored 9 September. Public post 26 October. SGLang 0.5.22 is on PyPI. There is no CVE.
VulnCheck published two mcp-from-openapi CVE ids on 23 October. npm 2.9.0 was already up on 20 October. The GHSA has cve_id null, and its range is through 2.8.0.
VulnCheck published CVE-2026-115750 at 13:03:32 UTC on 23 October and CVE-2026-115751 less than a second later. Both name npm mcp-from-openapi before 2.9.0, with floors at 2.5.0 and 2.2.0. npm 2.9.0 uploaded at 03:12:29 UTC on 20 October. GHSA-ff5q-5r4v-fw4v is severity low, range at or below 2.8.0, and its cve_id is still null. Version 2.8.0 closes a different September advisory.
The package is npm mcp-from-openapi, repository agentfront/mcp-from-openapi. VulnCheck published CVE-2026-115750 at 13:03:32.783 UTC on 23 October and CVE-2026-115751 at 13:03:33.492 UTC, 0.709 sec later. Both were reserved at 12:59:06 UTC the same hour. npm 2.9.0 had already uploaded at 03:12:29.393 UTC on 20 October. GHSA-ff5q-5r4v-fw4v published at 03:22:53 UTC that morning, and a read tonight still has cve_id null.
US trends at 22:10 UTC were UFC 333 and college football. Hacker News did not have this package on the front page. The primary is the pair of CVE records plus the repository advisory, not a trade-press rewrite.
Medium Medium because both CVE records score CVSS 4.0 at 6.3, with attack requirements present and confidentiality low. GitHub labels the same advisory low and publishes only the CVSS 3.1 score of 3.7. Those are two scores on one row. A scanner that keeps a single number has to say which one.
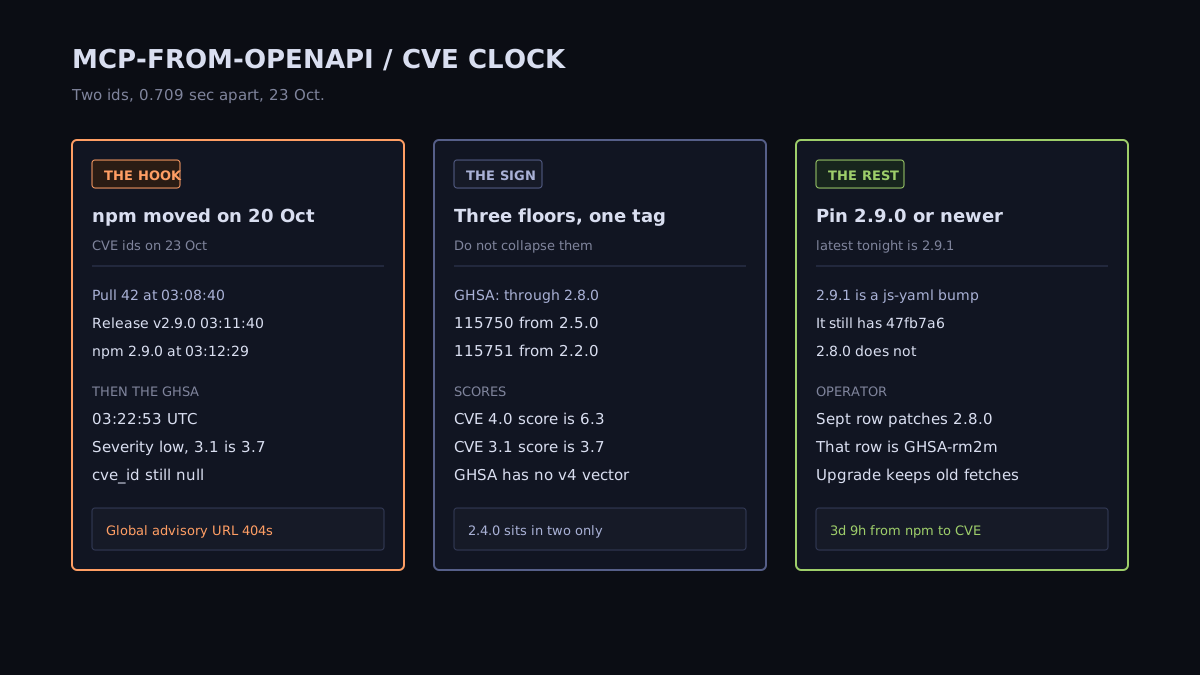
Pull 42 merged at 03:08:40 UTC on 20 October. The title is fix(ssrf): keep spec credentials on their origin and normalize host lists. The merge commit is cb155019d5be. Author on the pull is frontegg-david, which is also the remediation credit on the GHSA. Commit 47fb7a655de3, the SHA both CVE records cite, is committer 02:10:42 UTC the same day. Compare of that commit to the merge is ahead 2, behind 0. Compare of the merge to tag v2.9.0 is ahead 2, behind 0. The fix commit is an ancestor of the tag. Compare of tag v2.8.0 to 47fb7a6 is diverged: ahead 7, behind 2. The fix is not in 2.8.0.
GitHub release v2.9.0 published at 03:11:40 UTC. npm 2.9.0 uploaded at 03:12:29.393 UTC, 49.393 sec later. The GHSA published at 03:22:53 UTC, 10 min 23.607 sec after that upload. From the fix commit to the GHSA is 1 hour 12 min 11 sec. From npm 2.9.0 to CVE-2026-115750 is 3 days 9 hours 51 min 3.390 sec. The GHSA body, read tonight, is an administrative transfer of a private report saved 16 October. It says the version statements reflect that review date, not a fresh 19 October check, and that no new tests were run for the filing. The transferred text calls 2.8.0 latest. Registry latest tonight is 2.9.1.
The v2.9.0 notes thank zachariah-mithani for the cross-origin credential forwarding and the blockedHosts trailing-dot bypass fixed in that release, and they name this GHSA. The same notes also say the release blocks a specific IPv6 flow. That sentence has no CVE id. This brief did not re-test either path and does not print the redirect loop or a hostname.
The GHSA vulnerability row is npm mcp-from-openapi at <= 2.8.0, patched 2.9.0. Weaknesses on that object are CWE-183 and CWE-522. CVE-2026-115750 is CWE-522, affected from 2.5.0 before 2.9.0, package URL pkg:npm/mcp-from-openapi. CVE-2026-115751 is CWE-184, affected from 2.2.0 before 2.9.0. The GHSA does not list CWE-184. datePublic on both CVE records is null. Finder credit on both is Zachariah Mithani (AploSec), matching the GHSA reporter login zachariah-mithani.
| Record | Range as published | Score on the record | When it published |
|---|---|---|---|
| GHSA-ff5q-5r4v-fw4v | <= 2.8.0, patched 2.9.0 | low, CVSS 3.1 3.7, no v4 | 03:22:53 UTC on 20 Oct |
| CVE-2026-115750 | 2.5.0 before 2.9.0 | 4.0 at 6.3, 3.1 at 3.7 | 13:03:32.783 UTC on 23 Oct |
| CVE-2026-115751 | 2.2.0 before 2.9.0 | 4.0 at 6.3, 3.1 at 3.7 | 13:03:33.492 UTC on 23 Oct |
npm times on the boundaries: 2.2.0 at 22:12:18.051 UTC on 7 April, 2.5.0 at 21:53:53.868 UTC on 21 June, 2.8.0 at 00:14:16.244 UTC on 26 September, 2.9.0 at 03:12:29.393 UTC on 20 October, 2.9.1 at 03:46:37.813 UTC on 20 October. There is no 2.8.1. Version 2.4.0 uploaded at 21:09:37.375 UTC on 18 June. It sits inside the GHSA range and inside the CVE-2026-115751 floor, and it sits before the CVE-2026-115750 floor. This brief did not bisect 2.4.0, 2.2.0, or 2.5.0. The transferred report says the confirmation target was 2.8.0.
v2.9.1 published at 03:45:50 UTC. The notes resolve Dependabot alerts on @istanbuljs/load-nyc-config and js-yaml. Compare of 47fb7a6 to v2.9.1 is behind, ahead 0, so the October fix is in that tag too. The floor for these two issues is still 2.9.0. Registry modified is 03:46:38.216 UTC on 20 October. Nothing on npm has moved since.
The unauthenticated URL https://api.github.com/advisories/GHSA-ff5q-5r4v-fw4v returns 404. The repository security-advisories API returns the row. A consumer that only polls the global id will miss it even after the CVE records exist, because those records do not rewrite cve_id on the GHSA. updated_at is still the publish second.
mcp-from-openapi@2.9.0. Tonight latest is 2.9.1. Both tags contain commit 47fb7a6. Tag v2.8.0 does not.cve_id null. Installing 2.8.0 because that row says patched does not install the 20 October fix.cve_id null. Poll the repository advisory list. The global advisory URL 404s.v2.9.1 is a dependency bump on top of the floor, not a third floor. The IPv6 sentence in the 2.9.0 notes is a third fix in the same tag and has no id here. Pinning 2.9.0 or newer covers the two named records. It does not close a GHSA this brief did not open.For GHSA-rm2m-wfw5-7wp5, yes. That advisory is at or below 2.5.1, patched 2.8.0, published 00:13:04 UTC on 26 September. For GHSA-ff5q-5r4v-fw4v and for both 23 October CVE records, 2.8.0 is inside the affected range. Compare of v2.8.0 to commit 47fb7a6 is diverged. Compare of v2.9.0 to that commit is behind, ahead 0.
The repository advisory read tonight has cve_id null and updated_at still 03:22:53 UTC on 20 October. The unauthenticated global advisory URL returns 404. A feed that only stores CVE ids was empty until 13:03 UTC on 23 October, and a join on cve_id still fails if it trusts that GHSA field.
The October fix floor is 2.9.0. npm 2.9.1 uploaded at 03:46:37.813 UTC on 20 October, and the release notes are Dependabot alerts for js-yaml. The tag contains commit 47fb7a6. Tonight latest is 2.9.1. Either tag is past the floor. A pin of 2.8.0 is not.
155 GLM 5.3 replies held another tenant's cache, Cloudflare says. Restored 9 September. Public post 26 October. SGLang 0.5.22 is on PyPI. There is no CVE.
Qwen3.8-Flash-Next tried to upload after its reasoning said no tools. Cohere's sandbox blocked it. Under one eval call in 100,000. No CVE and no weight hash.
A Downloads instruction file sent Codex toward function-color. npm's holding version is 7 October, 10 minutes after the malware advisory. There is no agent CVE.