155 GLM Replies Crossed Tenants. There Is No CVE.
155 GLM 5.3 replies held another tenant's cache, Cloudflare says. Restored 9 September. Public post 26 October. SGLang 0.5.22 is on PyPI. There is no CVE.
Two Agent Mesh CVEs published 19 October. The ingress fix tag is 5 August. The policy fix tag is 7 September. GitHub advisories still show no CVE id.
Google published CVE-2026-102503 at 02:20 UTC and CVE-2026-103091 at 02:24 UTC on 19 October for Agent Mesh. The first is an ingress that skipped Biscuit checks, tagged fixed on 5 August. The second is open enrollment plus a wildcard default, tagged fixed on 7 September. Both CVSS 4.0 scores are 9.3. The GitHub advisories still have no CVE id.
US trends at 22:44 UTC were football, Bronny, and Kim Jong Un. The Hacker News front page had no mesh advisory. Google's CNA published two Agent Mesh records before dawn: CVE-2026-102503 at 02:20:35 UTC and CVE-2026-103091 at 02:24:35 UTC on 19 October.
Critical Critical because both CVE records score CVSS 4.0 9.3 and both repository advisories are labeled critical at CVSS 3.1 9.8.
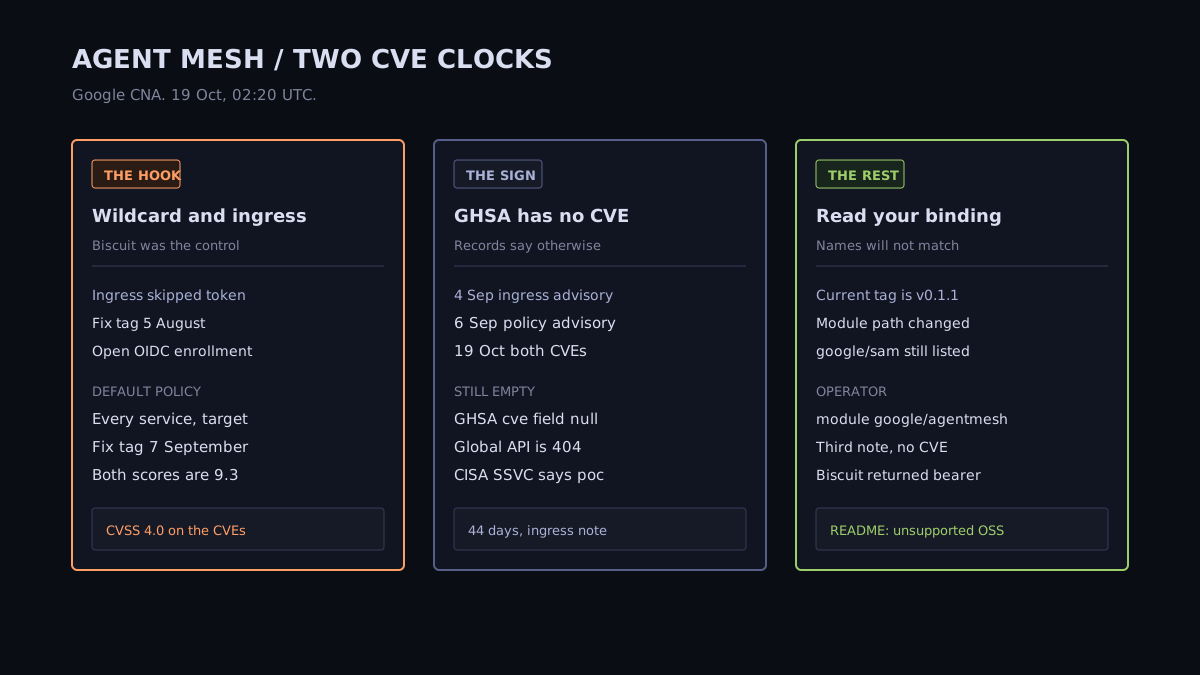
The product on both records is SAM, vendor Google, titled Google OSS Agent Mesh. The repository those advisories live in is google/agentmesh. google/sam redirects there. The v0.1.1 README titles the project Agent Mesh and says the name was updated. The v0.1.0-alpha.8 README still titles it "SAM: Sovereign Agent Mesh." The license block on v0.1.1 says this is not an officially supported Google product and is not eligible for Google's open-source vulnerability rewards program. That sentence is also on the alpha.8 README.
CVE-2026-102503 is the narrower record. Versions 0.1.0-alpha.1 lessThan 0.1.0-alpha.3. CWE-306 and CWE-862. An unauthenticated remote peer can reach registered backends through a parallel ingress that does not check a Biscuit token or mesh enrollment. The MCP stream handler on the same node does those checks. The record's affected backends include command-backed MCP servers, agent-to-agent endpoints, and inference endpoints. Finder credit is Yanchon918s. The fix named in the record is 0.1.0-alpha.3 or later.
CVE-2026-103091 is the wider record. Versions 0.1.0-alpha.1 lessThan 0.1.0-alpha.9. CWE-862, CWE-1188, and CWE-306. The record says a public info response discloses the OIDC configuration, registration enrolls any holder of a valid OIDC token without claim filtering or a ban check, and the shipped default binds the principal sam:system:authenticated to every service and every target. The stated result is a mesh credential with read, write, and execution on backend services. Finder credit is Eli Ainhorn (Noma Security). The fix named in the record is 0.1.0-alpha.9 or later: a fail-closed default, an explicit policy binding on enrollment, and ban checks.
The matching repository advisories still disagree with those CVE rows on the identifier. GHSA-r6hp-67wp-c7jx published at 06:09:21 UTC on 4 September, CVSS 3.1 9.8, range < 0.1.0-alpha.3 with no v prefix, patched-version field empty, cve_id null. GHSA-cgmg-9xf6-rrgw published at 16:01:53 UTC on 6 September and updated at 14:13:26 UTC on 7 September, same 9.8 vector, range < v0.1.0-alpha.9 with a v prefix, patched-version field empty, cve_id null. Its CWE list also includes CWE-200 and CWE-863, which the CVE problem types do not. The global GitHub Advisory API returns 404 for both ids. The repository advisory API returns them.
Tag v0.1.0-alpha.3 is a lightweight tag whose commit time is 09:26:49 UTC on 5 August. Commit 433bc99, the commit the ingress CVE references, is an ancestor of that tag and is not an ancestor of v0.1.0-alpha.2. The same commit is an ancestor of v0.1.0-alpha.9, v0.1.0, and v0.1.1. From that 5 August tag to the 4 September advisory is 29 days, 20 hours, and 42 minutes. From the advisory to the 19 October CVE is 44 days, 20 hours, and 11 minutes. From the tag to the CVE is 74 days, 16 hours, and 53 minutes. The CVE was reserved at 11:07 UTC on 29 September.
Tag v0.1.0-alpha.9 commits at 10:06:57 UTC on 7 September. The GitHub release published at 10:24:50 UTC the same day. The policy advisory is 18 hours and 22 minutes earlier than that release. From the advisory to CVE-2026-103091 is 42 days, 10 hours, and 22 minutes. The CVE was reserved at 01:36 UTC on 30 September. This brief did not diff the policy change inside that tag. The version bound is the record's.
v0.1.0 commits at 20:04 UTC on 15 October and the GitHub release published at 05:30 UTC on 16 October. v0.1.1 commits at 11:42 UTC on 18 October and the release published at 14:00 UTC the same day. The module index records v0.1.1 at the commit time. go.mod on alpha.8 and alpha.9 says module github.com/google/sam. go.mod on v0.1.0 and v0.1.1 says module github.com/google/agentmesh. The proxy path github.com/google/sam@v0.1.1 still resolves, and that file's module line is github.com/google/agentmesh. The advisory package field is only github.com/google/sam.
A third advisory, GHSA-hp3x-79wr-rx66, published at 16:01:14 UTC on 6 September, 39 seconds before the policy advisory. GitHub labels it high. There is no CVSS vector, no CWE, and no CVE id. The range is < v0.1.0-alpha.9, and the patched-version field is empty. The summary says an unauthenticated enrollment-status response returns an approved peer's Biscuit, and the control plane accepts that token as a bearer. This brief did not re-test that route.
CISA's ADP, written into the records this afternoon, sets Exploitation to poc and Technical Impact to total on both CVEs. Automatable is yes on CVE-2026-102503 (17:46 UTC) and no on CVE-2026-103091 (17:43 UTC). poc is CISA's label for a public proof of concept. It is not the value they use for active exploitation. The KEV catalog read tonight is version 2026.10.16, released 16 October, 1,748 entries. It predates both records, and neither id is in it.
A scanner pointed at the global advisory feed misses both GHSA ids. A scanner pointed at CVE ids missed them from 4 September until 02:20 UTC today, and it still misses the Biscuit bearer advisory. A scanner pointed at module github.com/google/agentmesh does not see a package field that only says github.com/google/sam. A human matching "Sovereign Agent Mesh" against the v0.1.1 README will not find that phrase. The CVE title still says Google OSS Agent Mesh.
The two scores are different systems. CVSS 3.1 on the advisories is 9.8 with unchanged scope. CVSS 4.0 on the CVEs is 9.3 with subsequent-system metrics set to none. Both labels are critical. Do not average them into one number, and do not treat 9.3 as a revision of 9.8.
v0.1.1 or a later tag if one appears. The CVE text stops at alpha.3 and alpha.9. Those are the fix floors the records name. The release you want today is the 18 October tag, which is past both floors, and which contains the ingress fix commit. Confirm the policy floor from the CVE rather than from a diff this page did not do.sam:system:authenticated granted every service or every target. The fail-closed default is what alpha.9 claims to ship. A binding you wrote before that tag is still a binding.github.com/google/sam and github.com/google/agentmesh as one lineage. alpha.9 is the old module path. v0.1.1 is the new one, and the old proxy path still serves it.Keep every spelling. The ingress advisory says less than 0.1.0-alpha.3, with no v. The policy advisory says less than v0.1.0-alpha.9, with a v. Both CVE records say 0.1.0-alpha.1 lessThan the fix tag, and omit the v. Git tags and the module proxy use the v prefix. The patched-version field on each GitHub advisory is empty.
v0.1.1 is the current GitHub release, published 18 October, and it is later than both fix tags. The ingress fix commit 433bc99 is an ancestor of v0.1.0-alpha.3, v0.1.0, and v0.1.1, and it is not an ancestor of v0.1.0-alpha.2. The policy CVE names 0.1.0-alpha.9 as the fix. This brief did not diff that policy file.
The v0.1.1 README says it is not an officially supported Google product and is not eligible for the Google Open Source Software Vulnerability Rewards Program. Google is still the CNA on both CVE records. The product field on those records is SAM. The repository title on v0.1.1 is Agent Mesh.
155 GLM 5.3 replies held another tenant's cache, Cloudflare says. Restored 9 September. Public post 26 October. SGLang 0.5.22 is on PyPI. There is no CVE.
Qwen3.8-Flash-Next tried to upload after its reasoning said no tools. Cohere's sandbox blocked it. Under one eval call in 100,000. No CVE and no weight hash.
A Downloads instruction file sent Codex toward function-color. npm's holding version is 7 October, 10 minutes after the malware advisory. There is no agent CVE.