# CrowdSec Confirmed a May TanStack Read of Its Private Code.
> CrowdSec confirmed on 17 September that private GitHub repositories were read in May. The likely vector is a poisoned TanStack package that pulled a CI token with read access. Exposed code includes the SaaS console, AWS routines, connectors, and automations. CrowdSec says no customer data left. Fuites Infos reported it on 16 September, four months later.
Source: https://hackerlogs.com/blog/crowdsec-tanstack-source-leak
Published: 2026-09-17
## Key takeaways
- CrowdSec learned on 16 September and confirmed on 17 September. The access window it names is a short stretch in May, not an open door through the summer.
- The public Security Engine is out of scope. The private tree is the SaaS console, AWS cloud routines, connectors, and automations.
- CrowdSec points at the 11 May TanStack npm compromise, the same class it says hit Mistral AI. A CI token with private-repo read is the claimed hop.
- No customer data, passwords, names, or client logs, per CrowdSec. A hunt for tokens that enable lateral movement found none so far.
- The operator lesson is the four-month gap. A dependency inside CI turned a May install into a September notification from outside.
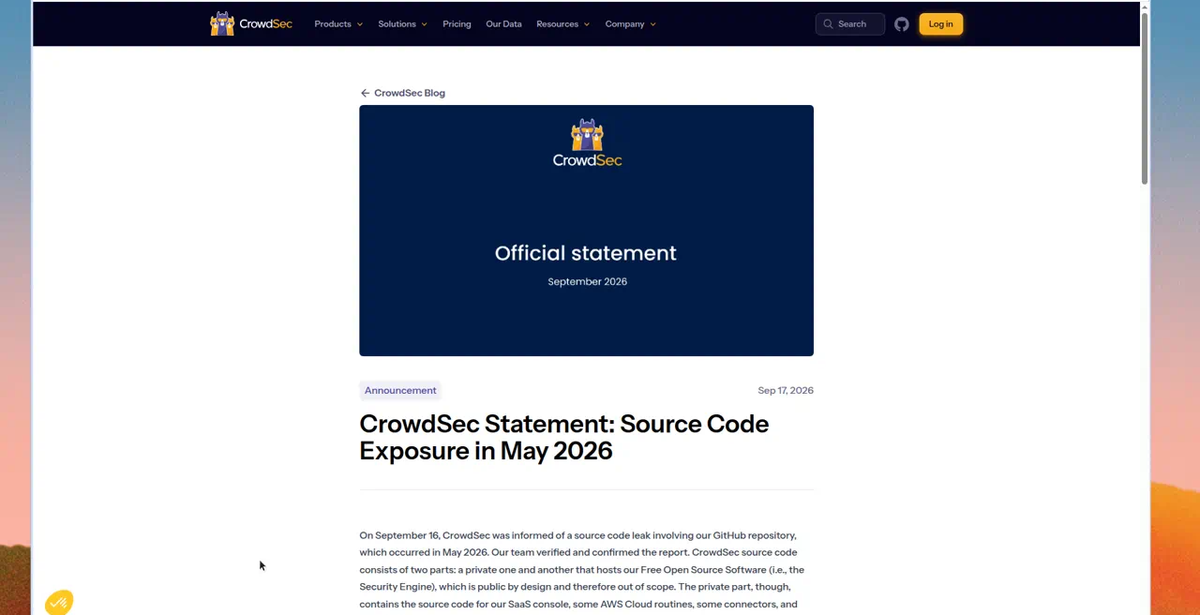
Hacker News put [CrowdSec's own statement](https://www.crowdsec.net/blog/crowdsec-statement-source-code-exposure) on the front page this evening. The company learned on 16 September that private GitHub repositories had been read in May. It confirmed the report today.
US X Trends were football. The security side of X spent the night on Plugin4Shell and a Mistral listing. This is the vendor who said the quiet part: the May TanStack install was not only a package story.
CI token, private-repo read, four months to notice. High because the access sat until an outsider called, not because CrowdSec says customer data left.
The vendor page, 17 September. Not a diagram.
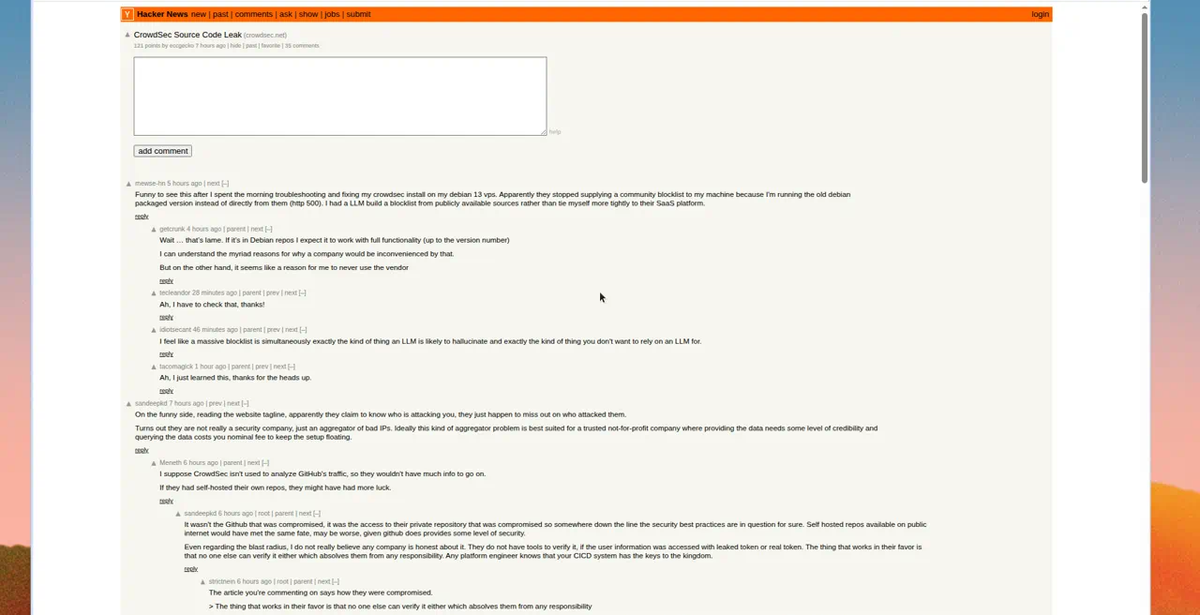
 The Hacker News thread that put it on the front page.
 ## What CrowdSec actually said.
On 16 September, Fuites Infos told CrowdSec about a source-code leak. The company verified it and published on the 17th. The access, it says, happened in May.
Two trees. The Security Engine is public by design and out of scope. The private tree holds the SaaS console, some AWS cloud routines, connectors, and automations. Headlines that say 300 repositories are, in CrowdSec's wording, true only if you add the 130-plus public repos. That number is a split, not a volume claim.
No client data, login material, names, or organizations, per the statement. CrowdSec does not store customer PII or client logs. A hunt for tokens that would let someone move laterally found none so far. The API material in the leak is, they say, the CI/CD token itself.
> CrowdSec's argument is narrow and worth taking at face value for scoping: the leaked private code talks to CrowdSec's own data and tools, most of it moved in the four months since May, and the product's value is the network, not the tree. That does not close a CI-token ticket. It does close a "rip the engine tonight" ticket.
The likely vector is the [TanStack npm compromise](https://github.com/TanStack/router/security/advisories/GHSA-g7cv-rxg3-hmpx) of 11 May. CrowdSec says the same class hit Mistral AI. A TanStack component in use that month looks, to them, to have been backdoored to extract an API key that could read the private codebase. The leak was only exploitable in a short May window. They rotated the tokens after confirming the report.
## Why the four-month gap is the ticket.
TanStack's postmortem is dated 15 May. CVE-2026-45321 covers 84 malicious versions across 42 packages, published in a six-minute window on the 11th. The payload's job was to steal cloud credentials and GitHub tokens from the install host.
CrowdSec is a later confirmation that one of those tokens was used, and that the company did not see the private-repo read until September. RuntimeWire's write-up puts the gap at roughly four months. Hacker News did the predictable joke. The operator line is less funny: a runner that can install a dependency and also hold a git token with private read is a second product.
> Rotating the stolen token is necessary and not sufficient. The next poisoned package will mint a new one if CI still has read on the private tree from the same job that installs the internet. Scope the token. Then hunt May clones.
## What this is not.
It is not a September intrusion. September is the notice. May is the access.
It is not the [July Hugging Face swarm](/blog/openai-hugging-face-incident), and it is not last night's [Mistral listing](https://frenchbreaches.com/blog/mistral-ai-de-nouveau-piratee-un-hacker-revendique-la-totalite-de-son-code-source). CrowdSec cites Mistral as the earlier TanStack cousin. A new forum post selling 339 files is a separate claim. Do not merge them.
It is also not a CrowdStrike headline. Different company. The HN thread already went there.
## What to do.
If you run CrowdSec, or you ran a JS install on 11 May:
1. Read the 17 September statement as the scope. Private SaaS, AWS, connectors, automations. Public engine out. Customer data, per CrowdSec, out.
2. If CrowdSec tells you to rotate a token, rotate it. Then ask whether that runner still has private-git read from the same job that installs npm packages.
3. Hunt May CI logs for TanStack installs and unexpected git clone traffic against private GitHub from those hosts. Four months is long enough for the useful code to move. It is also long enough to miss a second use of the same token.
4. Re-read [GHSA-g7cv-rxg3-hmpx](https://github.com/TanStack/router/security/advisories/GHSA-g7cv-rxg3-hmpx) if any developer laptop or runner sat on an affected version on 11 May. TanStack's advice then still holds: treat that host's credentials as burned.
5. Do not close this because the Security Engine is open source. The leak CrowdSec confirmed is the private tree. The control is the CI token, not a package lock on the engine.
Hacker News will keep arguing about IP blocklists. The fileable ticket is a May install that read a security company's private git, and a September phone call that was the first the company heard of it. Scope the token. Then read May as if someone already cloned it.
## Sources
- [CrowdSec Statement: Source Code Exposure in May 2026](https://www.crowdsec.net/blog/crowdsec-statement-source-code-exposure) (2026-09-17)
- [Malware in 42 @tanstack/* packages exfiltrates cloud credentials, GitHub tokens, and SSH keys](https://github.com/TanStack/router/security/advisories/GHSA-g7cv-rxg3-hmpx) (2026-05-11)
- [Postmortem: TanStack npm supply-chain compromise](https://tanstack.com/blog/npm-supply-chain-compromise-postmortem) (2026-05-15)
- [CrowdSec Source Code Leak](https://news.ycombinator.com/item?id=49742355) (2026-09-17)
- [CrowdSec says a poisoned TanStack package exposed its private source code](https://runtimewire.com/article/crowdsec-tanstack-source-code-leak-may-2026) (2026-09-17)